A suspicious process does not always arrive as an unfamiliar executable. Sometimes the software is already installed, used by administrators, and signed by a trusted publisher. The security problem begins when someone uses those legitimate capabilities for an unauthorized purpose.
That is the idea behind Living off the Land (LOTL). Understanding it means looking beyond the name of a program and asking what it did, who started it, and whether that behavior belongs in the environment. This guide explains the concept, the terminology, and the defensive questions worth asking before introducing LOTL Reference, my own project for exploring the subject.
What is Living off the Land?
In cybersecurity, Living off the Land describes the abuse of native tools and processes to carry out malicious activity while blending into normal operations. An intruder may reuse the environment’s existing capabilities instead of deploying a separate custom tool for every task. The joint LOTL guidance from CISA, NSA, FBI, ASD’s ACSC and international partners describes its use across Windows, Linux, macOS, cloud, and hybrid environments.
Think about the difference between a tool and the authority to use it. A shell can run a maintenance script. A transfer utility can retrieve a business file. A scheduler can start a routine job. Those capabilities do not become harmless simply because the operating system provides them. Their security significance depends on the action, permissions, and surrounding workflow.
LOTL is therefore a way of operating, rather than the name of a particular vulnerability or malware family. It can be one part of a larger intrusion. It also does not tell you how the intruder first gained access; phishing, stolen credentials, or an exploited application may precede the use of legitimate tooling.
LOLBins, LOLBAS, and the vocabulary
A LOLBin is a “Living off the Land binary”: a legitimate executable with capabilities that can be repurposed. The LOLBAS project documents Windows binaries, scripts, and libraries with security-relevant use cases. Its scope includes more than executable files, which is why LOLBAS and LOLBin are related terms rather than interchangeable names.
Several distinctions help when reading research:
| Term | What it tells you |
|---|---|
| LOTL | The broader approach of reusing legitimate capabilities for malicious activity. |
| LOLBin | A legitimate binary whose functionality can be repurposed. |
| LOLBAS | A community reference covering Windows binaries, scripts, and libraries. |
| Abuse case | A particular behavior and the conditions that make it possible. |
| Detection | Evidence or logic that helps identify a behavior; it still needs environmental context. |
A catalog entry is a research lead. It does not mean the program is malicious, that every installation is exploitable, or that every execution should trigger an incident.
Why legitimate software can be useful to an intruder
Existing tools reduce the need to introduce unfamiliar software and can resemble ordinary administrative activity. The joint guidance highlights weaknesses such as missing baselines and limited visibility that make this overlap difficult to investigate. That is a problem of context and controls, not a guarantee that native tools bypass security products. Read the joint guidance.
A related issue is System Binary Proxy Execution. MITRE ATT&CK tracks this under T1218: a trusted system binary can be used to execute other content. The host program’s reputation does not establish the intent of the content it loads or the person invoking it.
A digital signature is useful evidence about the signed file’s publisher and integrity. It does not authorize a particular command, validate an external input, or prove that a child process belongs to a legitimate business task. Checking the signature should be one step in the investigation.
Living off the Land is not the same as fileless malware
The terms often appear together, but they describe different aspects of an operation. LOTL concerns the legitimate capabilities being reused. “Fileless” concerns how malicious components execute or persist, often with an emphasis on memory or mechanisms such as the registry. Microsoft’s technical discussion of fileless malware illustrates how native tools can participate in those chains.
An operation can use legitimate tools and still download a file, write a script, create a task, or leave other artifacts. Conversely, describing a component as fileless does not establish that the whole intrusion avoided the filesystem. Neither label means there is no evidence to collect.
For an analyst, the useful questions are concrete: what executed, what input did it receive, what changed, and which logs recorded it? A fashionable label is less useful than a reconstructable sequence of events.
This is not only a Windows topic
Windows has an extensive public reference ecosystem, but the underlying idea is broader. GTFOBins documents Unix-like utilities whose legitimate features can bypass local restrictions in particular configurations. The project explicitly explains that the listed programs are not inherently vulnerable and that it is not a catalog of software exploits.
Permissions are central here. Finding a utility on a Linux host does not automatically provide elevated privileges. Its execution context, delegated administrative rights, SUID configuration, or Linux capabilities may determine whether a documented behavior is relevant. An example that works under one permission model may fail under another.
For macOS, LOOBins catalogs native binaries and security-relevant uses. Scripts, interpreters, and administrative interfaces also deserve attention: MITRE’s Command and Scripting Interpreter technique, T1059, covers several platforms and interpreter families. Mapping should follow the observed behavior rather than assigning every use of a familiar program the same technique ID.
Three examples of why context matters
The following scenarios are illustrative analyst exercises, not reports of specific incidents. None of the individual signals below establishes malicious intent by itself.
| Scenario | An expected explanation | A reason to investigate |
|---|---|---|
| A scripting interpreter runs | An approved maintenance job uses a known script under a documented service account. | A document application starts an interpreter that then contacts an unfamiliar destination. |
| A system utility loads a library | An approved application loads its expected component from its installation directory. | The utility loads a recently created library from a user-writable location. |
| An administrative utility transfers data | A deployment workflow retrieves a known package from an approved repository. | An unexpected account initiates a transfer, followed by execution of newly written content. |
In each case, start with a question that can be tested. Does a deployment record explain the timestamp? Is the account normally used on this device? Was the loaded file present before the process started? Does the destination belong to the expected workflow? The investigation becomes stronger when independent evidence supports the same explanation.
An unusual parent process is a lead, not a complete verdict. A trusted parent is not a universal exemption either. Document the expected workflow precisely enough that an exception explains why the activity is allowed.
What defenders should collect and correlate
The international guidance on event logging and threat detection emphasizes useful telemetry, central access and correlation, secure storage, and a detection strategy. For LOTL investigations, relevant sources can include process and command execution, PowerShell script and module logging, Linux activity, cloud API operations, and authentication events. Availability depends on the platform and enabled controls.
- Execution context: the account, device, parent process, command line, and privilege level.
- Inputs and outputs: scripts, loaded libraries, file creation, and configuration changes.
- Network context: destinations, timing, and the process responsible for a connection.
- Sequence: what happened before and after the alert, including sign-ins and administrative changes.
For example, a process name alone tells a narrow story. A timeline that connects an unexpected sign-in, a newly written script, and an unusual process chain gives the analyst several claims to verify. Missing telemetry should be recorded as a visibility gap rather than silently treated as evidence that nothing happened.
Logs must remain usable during an investigation. Define retention, protect them against tampering, and preserve enough identity and timing information to join related events. Collecting more data without a plan for searching it will not automatically improve detection. The logging guidance explains these operational requirements.
Reducing opportunity without breaking administration
Useful controls include restricting unnecessary execution, enforcing least privilege, and applying application-control policies appropriate to the environment. MITRE’s T1218 mitigations also discuss limiting tools that are not needed and controlling related network access. Policies need testing against legitimate applications and administrator workflows.
A practical review begins with ownership. Which team needs this capability? On which systems? Under which accounts? Once those questions have answers, the organization can constrain unnecessary access and monitor the workflows that remain.
Avoid treating a community list as a ready-made blocklist. Removing a necessary utility without understanding its dependencies can break operations. Allowing everything signed by a trusted vendor creates a different blind spot. Good policy is specific enough to preserve the required task while reducing unnecessary privilege and execution paths.
Related techniques need their own explanation
Research around trusted software also includes vulnerable drivers and library loading. LOLDrivers catalogs known vulnerable and malicious Windows drivers. Bring Your Own Vulnerable Driver (BYOVD) can involve introducing a driver, so it should not automatically be described as using only components already installed.
DLL hijacking concerns which library an application loads and whether an attacker can influence that choice. Trusted web services and risky file formats raise other questions about delivery, communication, and execution. These areas overlap with LOTL research, but each has different prerequisites and evidence.
There is also the reverse problem: harmless software can look suspicious. WTFBins documents benign applications with malware-like behavior to help improve hunting and detection. This is a useful reminder that a reference should help explain evidence, not replace judgment.
Introducing LOTL Reference
Disclosure: I built LOTL Reference as a searchable starting point for this research. My goal is to make it easier to move from a question about a platform or behavior to the relevant community documentation.
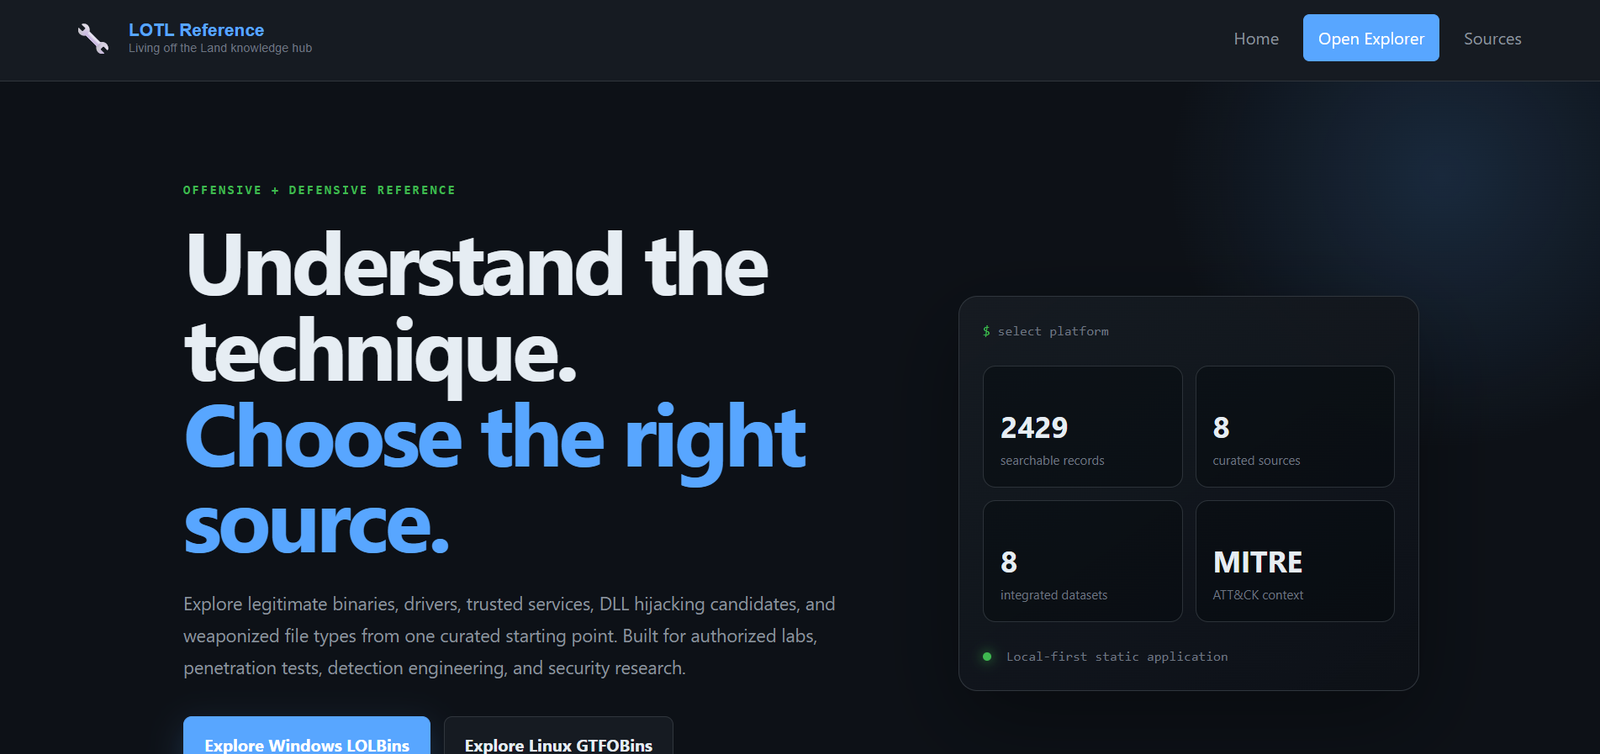
The interface brings together eight upstream datasets. At the time of review, it displayed 2,429 records; that figure describes the integrated snapshot and will change as the project develops. The sources cover different questions:
| Source | Research focus |
|---|---|
| LOLBAS | Windows binaries, scripts, and libraries. |
| GTFOBins | Unix-like utilities and configuration-dependent capabilities. |
| LOOBins | macOS native binaries. |
| LOLDrivers | Known vulnerable and malicious Windows drivers. |
| LOTS Project | Legitimate online services with documented abuse cases. |
| WTFBins | Benign applications that can create suspicious-looking telemetry. |
| HijackLibs | DLL hijacking candidates and associated reference material. |
| Filesec | File extensions and their security-relevant uses. |
In the explorer, you can select a dataset, search for a tool, and narrow the results using the available behavior filters. Opening a record shows its details and references. For example, searching the Windows dataset for Certutil opens an entry with its description, documented capabilities, ATT&CK links, detection references, and the original LOLBAS page.
A useful learning exercise is to choose one entry and explain its legitimate purpose before reading its abuse cases. Then identify the prerequisites, decide what evidence would distinguish expected use, and follow the original references. For a detection engineer, that becomes a starting point for a hypothesis to validate against local telemetry.
LOTL Reference is a knowledge hub. Reading an entry does not assess your system or confirm that a technique works there. The project preserves upstream ATT&CK mappings where provided; it also describes some GTFOBins mappings as conservative inferences and leaves entries without reliable mappings unmapped. Treat those labels as research context.
The underlying research belongs to the upstream maintainers and contributors. Follow their documentation for prerequisites, updates, and limitations. You can explore the project at livingofftheland.dev and use it to connect the theory in this article with a more focused question about your own authorized lab or defensive environment.

